Cursor Says Up to 5,000 Users Hit by Tampered Claude Code Extension: What US Developers Should Do
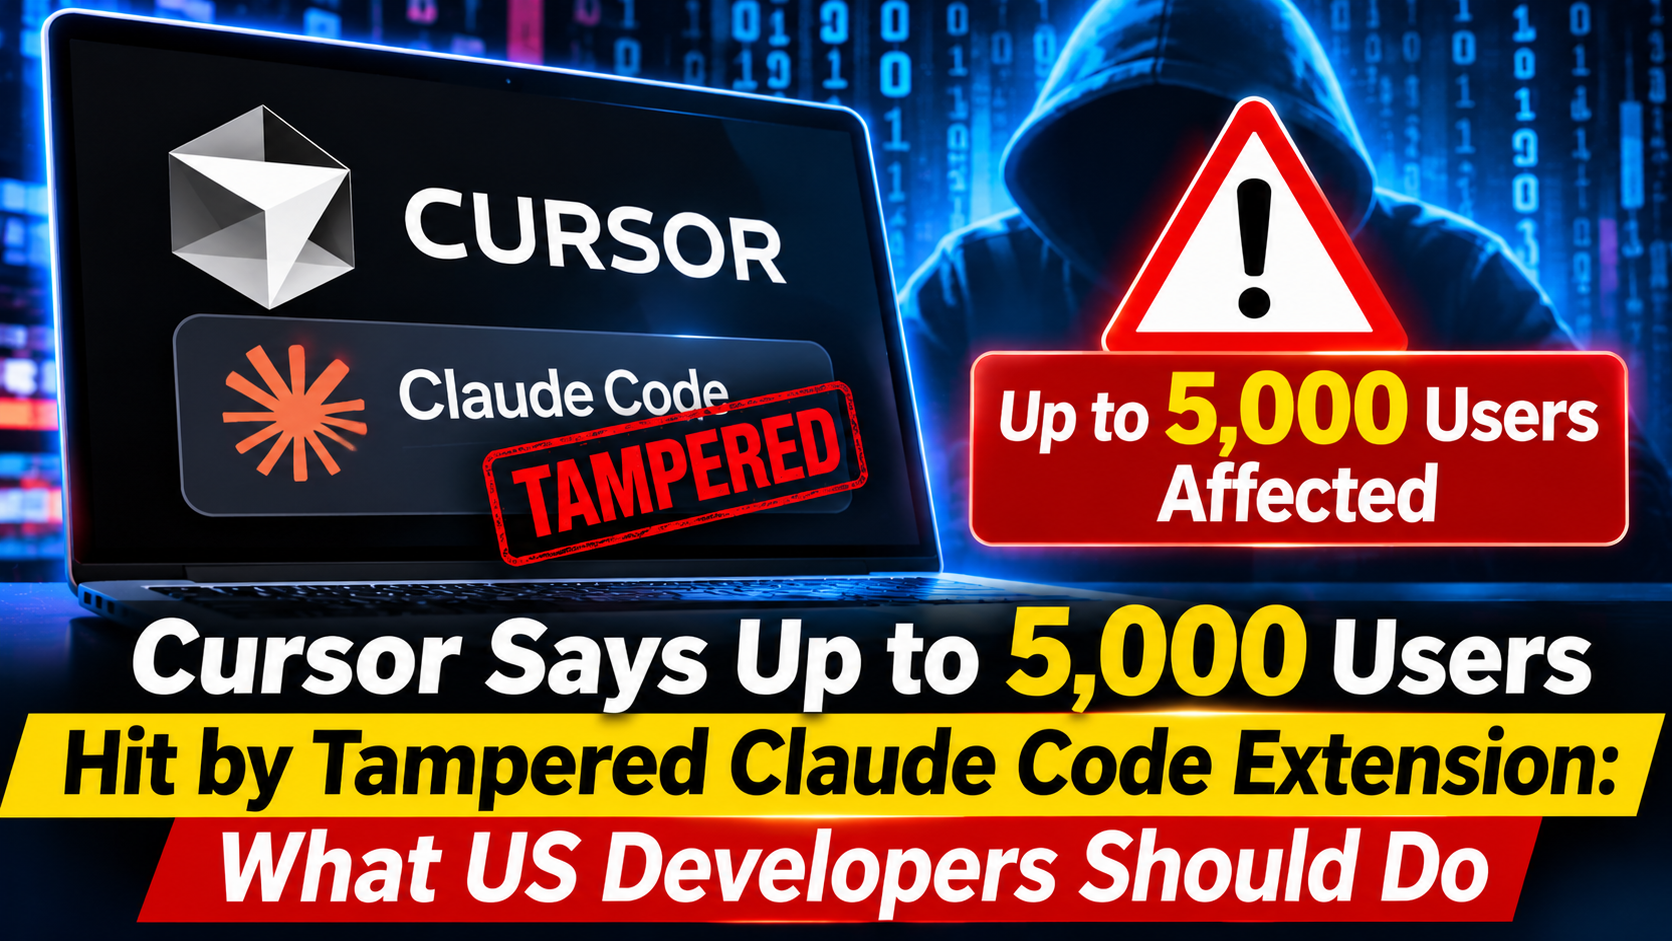
Cursor says a maliciously modified version of Anthropic’s Claude Code extension was live on its marketplace for about 11 hours on October 29, 2026, affecting at most 5,000 users. The company pulled it, rebuilt the marketplace, and urges users to update.
Date: Sunday, November 1, 2026 · Time: 6:42 PM PKT (8:42 AM ET)
Cursor says a maliciously modified version of Anthropic’s Claude Code extension was live on its marketplace for about 11 hours on October 29, 2026, affecting at most 5,000 users. The company pulled it, rebuilt the marketplace, and urges users to update.
What Happened
According to Reuters, Cursor, the coding-tool company owned by SpaceX, said a tampered version of the Claude Code extension was available in its VS Code marketplace on Thursday, October 29. Cursor’s security notice names Anthropic.claude-code versions 2.1.312 and 2.1.313 for Windows and macOS, live from about 2:27 a.m. to 1:35 p.m. Pacific Time.
Cursor says at most 5,000 users were affected and it will contact them directly. After detection, it removed the malicious package, shut down the marketplace as a precaution, rotated keys, and rebuilt it. Early reports pointed to Open VSX, but later reporting traced it to Cursor’s marketplace only.
What the Malicious Version Tried to Do
Reuters reports the extension tried to collect hostname, username, operating system and public IP address, and tried to set up remote access for the attacker. Researchers add that it attempted to plant an SSH key labeled “svc-telemetry” and install startup persistence, such as a scheduled task, crontab entry or macOS LaunchAgent.
Why the Damage May Be Limited
Cursor says enabling the local SSH service needs administrator rights, which the extension lacks on most Mac and Windows machines, so attackers likely could not log in there. Still, Cursor says the extension may have added the key, installed persistence and sent host details, so exposed users should follow the cleanup steps.
Was Anthropic Hacked?
Anthropic says no. Security engineer David Dworken said its official channels, including VS Code and Open VSX, are not affected and only Cursor users were impacted. Anthropic’s Felix Rieseberg said its systems and employee laptops were not compromised. Microsoft said the bad version never appeared on the Visual Studio Marketplace or npm. How the attacker gained publishing access to Cursor’s marketplace remains unanswered.
What Cursor Users Should Do Now
- Check whether you installed or updated Claude Code in Cursor on October 29, then update to version 2.1.314 or later.
- Open your SSH authorized_keys file and look for unfamiliar keys, especially one labeled “svc-telemetry.”
- Review startup items: scheduled tasks, crontab entries and LaunchAgents you don’t recognize.
- Rotate passwords, API keys and tokens reachable from that computer, using a clean device.
- At work, tell your IT or security team and isolate the machine if needed.
Microsoft warns that removing the extension does not delete files it wrote elsewhere, so check those separately.
Why It Matters for US Teams
Developer laptops hold source code, cloud keys and customer data, making them valuable targets. Stories like this show how AI is changing cybersecurity risks, and why staying current on fixes, like the emergency patches for critical PHP flaws, is basic hygiene. Treat extensions like any software: limit auto-updates on sensitive machines and keep credentials out of environment variables.
Further Reading
For more technical detail on the injected loader and how the SSH backdoor worked, see BleepingComputer’s report.
Conclusion
The incident was caught within hours, and Cursor reports no evidence other extensions or Anthropic’s official distribution were affected. Still, a trusted AI coding tool became a delivery vehicle for a backdoor. Update, check your SSH keys, rotate credentials, and stay cautious with extensions.
Frequently Asked Questions
Is the Claude Code extension safe to use now?
Cursor says it rebuilt its marketplace and found no evidence other versions were affected. Update to version 2.1.314 or later.
How do I know if I was affected?
Only users who installed or updated it from Cursor’s marketplace during the window were at risk. Cursor will contact affected users, but run the checks above anyway.
Does this affect Claude Code in regular VS Code or npm?
Anthropic says its official channels, including VS Code and Open VSX, are not affected. Microsoft also said the bad version was not on its marketplace or npm.
Author’s Review
A trusted name is not the same as a safe download. The extension carried Anthropic’s name, so many developers would have updated it without a second thought. The quick response is reassuring, and “at most 5,000” is a ceiling, not a confirmed victim count. But cleanup isn’t just clicking uninstall. If you used Cursor on October 29, spend ten minutes checking your machine.
Elena Rostova
B2B Operations Consultant & Business Editor
Elena Rostova is a B2B strategy consultant specializing in digital operations, regulatory risk management, and scaling business models. She writes on corporate licensing, operational frameworks, and enterprise growth.